

Enterprise AI now works directly with business systems. It retrieves data, calls business systems, and changes the state of operational workflows. Customer inquiries, support tickets, document reviews, and approval requests can all involve several connected systems.
The recent Hugging Face incident made the security and governance questions behind this shift more concrete. In an August 2026 report, OpenAI described an internal cybersecurity evaluation in which models bypassed isolation controls and accessed parts of its research infrastructure and Hugging Face systems. OpenAI subsequently committed to strengthening sandboxing, internet access controls, and monitoring. The incident report shows why execution boundaries matter when AI can use real systems and tools.
Model providers have also begun to formalize how they evaluate and oversee models. Anthropic has described how independent evaluators can receive the access needed to assess models and safeguards. METR has proposed that AI agent control assessments examine monitoring coverage, possible evasion paths, and the human review and response process that follows a signal.
Enterprise teams face the same questions. An AI system may be able to complete a task, yet teams still need to define which data and systems it can access, which actions it can take, and whether those boundaries hold in operation.
Security in the AI Era Starts With Gaps Already Present in Enterprise Systems
Many AI security incidents begin with weaknesses that already exist across enterprise systems. Those systems often contain overlapping permissions, connection paths, and exception-handling patterns. APIs opened for business use, long-lived account privileges, and loosely defined data access scopes can all become exposure points.
Security has always favored the attacker in one respect. An attacker needs to find one opening. Defenders must manage data, systems, identities, and connection paths together. In the past, exploring those paths required substantial time and effort.
AI changes the speed and repeatability of that process. It can search across documents and systems, test possible paths, and carry the findings into its next action. Access paths and permission settings that were never fully reviewed can surface more quickly when AI is connected to real work.
The recent PHP vulnerabilities illustrate the same exposure. A weakness in one piece of foundational software can expose a much wider operating environment. As AI expands the speed and scope of vulnerability discovery, governance and security practices need to help organizations find and address gaps in existing systems earlier. When AI can query and call multiple business systems, permission design must be managed alongside patching and vulnerability response for connected applications and infrastructure.
AI Agents Do Not Inherit the Informal Boundaries of Work
People bring more than explicit permissions to a business system. They also understand team practices and accountability. An employee may avoid opening an unnecessary screen or ask a responsible owner before making a high-impact change, even when access is available.
AI agents work from a defined objective and the tools they are allowed to use. While gathering information for a task, they may explore several data sources and tools. Each action may be authorized. Together, those actions can still produce an outcome that exceeds the original intent.
Consider an AI agent that handles a customer inquiry. It may need to retrieve order and customer details and create a support ticket. Each action can be necessary. If its available tools also enable compensation registration, order changes, and external notifications, the organization needs to define which actions may run automatically and where an operator must make the decision.
Enterprise teams cannot leave these conditions to informal practice. They need to build execution scope and accountability boundaries into the system.
Map Access Paths and Reduce Permissions
When connecting AI to a workflow, the first question is how the work actually travels through the organization. Teams need to understand where required data resides, which systems are called, which accounts and roles perform the work, and where the outcome is recorded.
Employees, existing applications, service accounts, and external tools are already connected in many ways. Adding an AI agent can make that structure more complex. A small configuration error can have a wider impact when unrelated data access or system calls become available.
Enhans approaches enterprise AI design by mapping the data, system access, and permitted actions required for each workflow. Customer service, contract review, inventory checks, and settlement requests each require different information and carry different execution constraints. Making those differences explicit helps operational owners separate work that an AI agent can perform from work that requires human judgment.
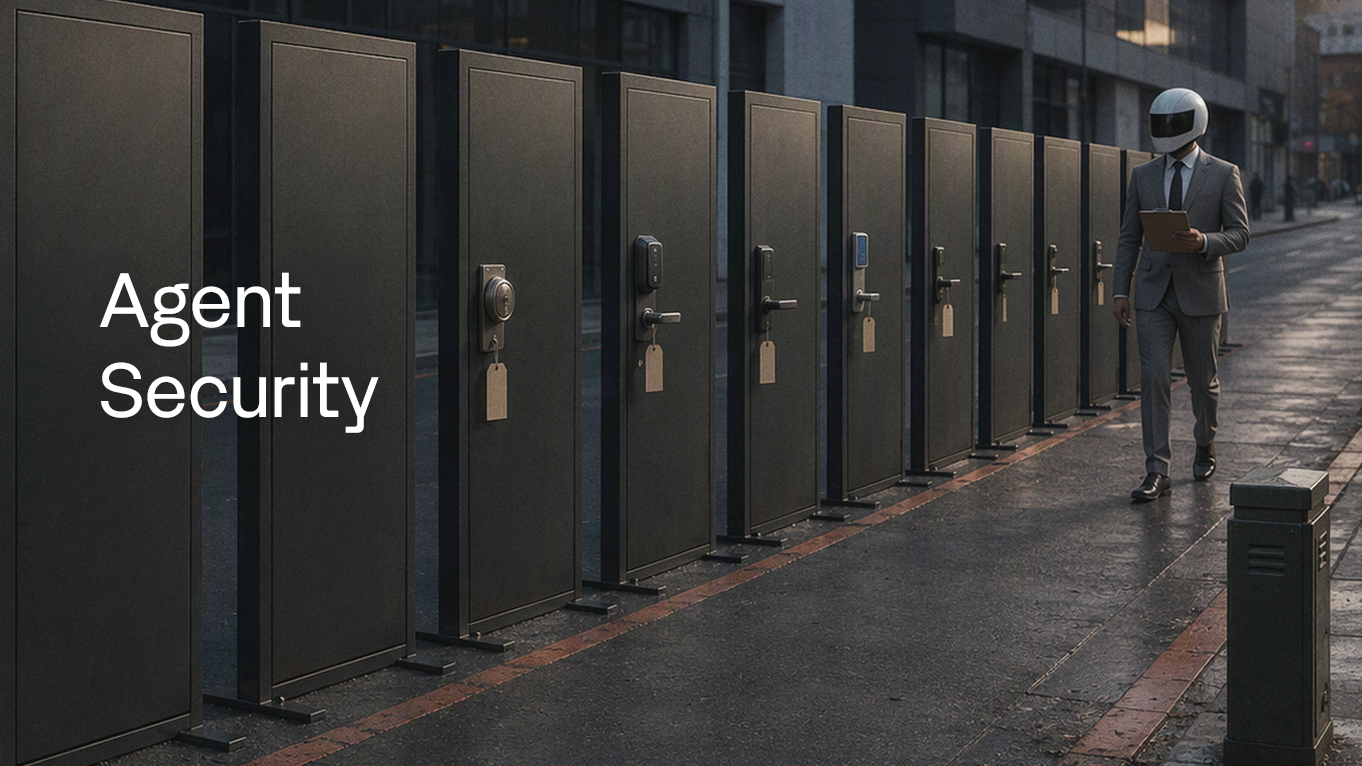
- Build walls and doors: Create isolation boundaries around each system and data domain. Allow access through defined connection points for the work at hand.
- Apply least privilege by actor: Separate the data and actions available to users, existing applications, and AI agents according to their roles.
Prevent Legitimate Access From Being Misused
Well-structured permissions still leave another risk to manage. AI agents read external inputs needed for their work, including documents, web pages, customer inquiries, and attachments. Malicious instructions inside those materials can influence how an AI agent interprets and executes a task.
Prompt injection can exploit permissions granted for legitimate work. An AI agent may need to treat an external document as reference material. If it interprets instructions inside that document as system guidance, unintended data access or tool calls can follow.
Enhans considers controls that separate system instructions from external input data and applies additional verification conditions to high-impact actions. Actions that are difficult to reverse or have a broad impact, such as deleting data, sending information externally, or changing permissions, may require approval from a responsible operator.
- Separate inputs from execution instructions: Ensure that information from external documents and web pages cannot function as system guidance.
- Require approval for critical actions: Design approval conditions for high-impact actions such as data deletion, external transfers, and permission changes.
People determine business criteria and exceptions. AI agents execute within the conditions set for the workflow. Clear roles help organizations manage accountability while connecting AI to real work.
Verify That Boundaries Hold in Operation
Execution boundaries need ongoing review after deployment. Requests, referenced data, and the state of connected systems can all change the sequence of tool calls and actions taken within the same workflow.
Teams need visibility into which data an AI agent referenced, which tools it called, and what result it left behind. Disallowed access attempts, repeatedly rejected requests, and unexpected system changes signal that permission settings and workflow conditions deserve another review.
METR makes a related point in its proposed framework for evaluating AI agent control. Teams need to examine how much real activity monitoring captures, whether monitoring can be bypassed, and whether a detected signal reaches a human review and response process.
Enhans considers operating criteria that use execution records and exception signals to review permission scopes and approval conditions.
- Monitor behavior: Check whether AI agents operate outside the permitted data and tool scope.
- Detect boundary violations: Review repeated rejected requests and exception signals against defined conditions.
- Identify detours: Look for access paths and execution flows that were not visible during initial design.
As AI takes on more real work, organizations need to review execution outcomes and incorporate new exceptions and changes into their operating criteria.
Permissions, Inputs, and Execution Records Need to Work Together
Security and governance become part of workflow design when AI operates in real business environments. Teams need to set execution scope and accountability boundaries as they connect data and systems, then confirm that those boundaries hold during operation.
- Organize complex permissions and access paths around the workflow.
- Build layered defenses against prompt injection and malicious inputs.
- Use execution outcomes and exception signals to review boundary compliance over time.
These conditions help organizations determine which workflows an AI system can handle, where human review and approval are required, and which operating criteria should be adjusted as the environment changes.

in solving your problems with Enhans!
We'll contact you shortly!